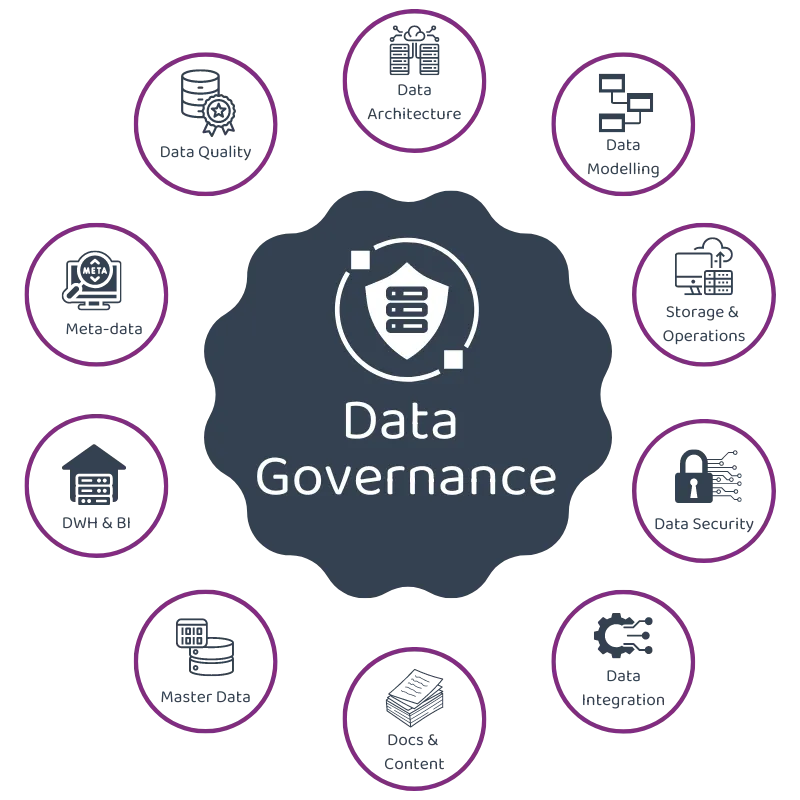
Data governance is how an organisation makes sure its data is accurate, secure and used appropriately. It covers who owns which data, the rules for quality and access, and how issues get fixed.
Governance has a reputation for bureaucracy, but done well it's practical and light-touch. This article explains why it matters and how to establish governance that people actually follow.
Why data governance matters
- Data quality: clear ownership and rules mean errors are caught and fixed at the source.
- Compliance: privacy and industry obligations are easier to meet when you know what data you hold, where it is and who can access it.
- Risk management: classifying sensitive data and controlling access reduces the impact of breaches and mistakes.
- Efficiency: people spend less time hunting for data or reconciling conflicting numbers.
- Strategic alignment: data investments focus on what the organisation needs.
- AI readiness: AI amplifies whatever data it's given, good or bad. Governance makes AI safer and more accurate.
Who does what
Governance works when responsibility sits with the people who know the data best:
- Data owners are senior business people accountable for a data domain, such as customer or finance data. They decide who may use it and what "good" looks like.
- Data stewards look after the data day to day: definitions, quality rules and fixing issues.
- Data consumers (analysts, report users, AI applications) find, request and use data within the agreed rules.
- A small central team sets the shared standards and tools, and keeps everyone moving.
This is often called federated governance: central standards for safety and quality, with ownership spread across the business so it doesn't become a bottleneck. It's the approach Microsoft recommends in its guidance for Microsoft Purview.
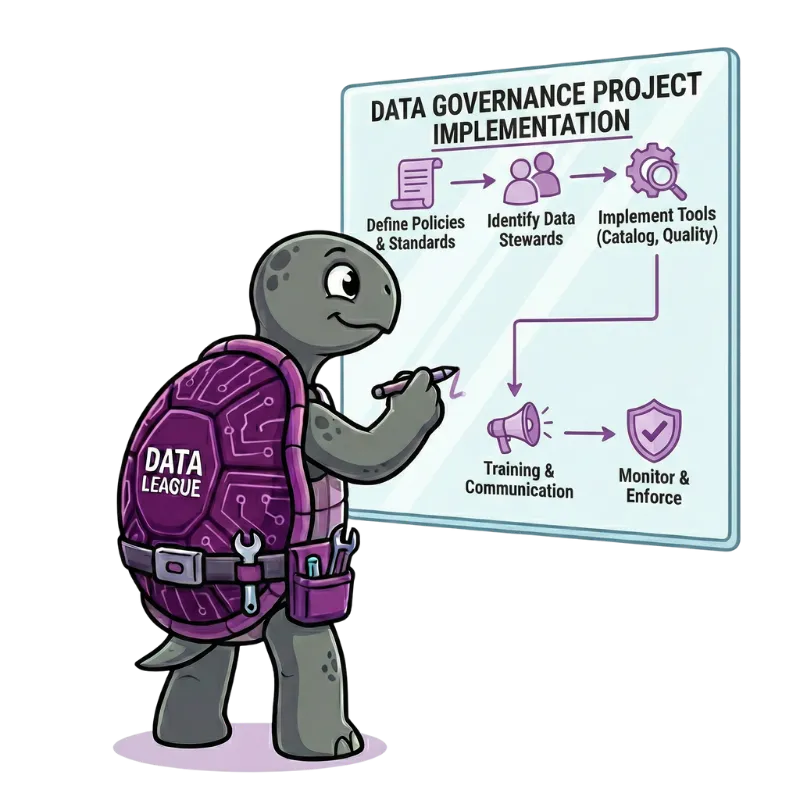
Establishing effective governance
- Get leadership support. A senior sponsor gives governance authority and keeps it connected to business priorities.
- Start with a simple framework. Define roles (owners and stewards), a small set of policies and a way to raise and resolve issues.
- Catalogue key data. Record your most important data sets, their owners and definitions in a business glossary and data catalogue.
- Name your critical data elements. These are the pieces of information that matter most, such as customer ID or account balance, which often appear under different names in different systems ("CustID" in one, "CID" in another). Defining each once lets you apply the same quality rules and access controls everywhere it appears.
- Set quality standards. Agree rules for your critical data elements and monitor them automatically, with dashboards that show trends.
- Secure sensitive data. Classify and label sensitive information, apply access controls and review them regularly.
- Manage the lifecycle. Define how long data is kept and how it's archived or deleted.
Australian privacy obligations
For any organisation covered by the Privacy Act 1988, governance is how you show you meet the 13 Australian Privacy Principles (APPs). Several map directly to governance work:
- APP 1 requires personal information to be managed in an open and transparent way.
- APP 6 sets out when personal information may be used or disclosed.
- APP 10 requires reasonable steps to make sure personal information is accurate, up to date and complete.
- APP 11 requires reasonable steps to protect personal information from misuse, interference and loss, and from unauthorised access, modification or disclosure.
- APP 12 covers people's right to access the personal information you hold about them.
The Notifiable Data Breaches scheme adds a clear test. A breach is an eligible data breach when three things are true:
- personal information has been accessed or disclosed without authorisation, or lost;
- this is likely to result in serious harm to one or more people;
- you haven't been able to prevent that risk with remedial action.
If you suspect one, you must take all reasonable steps to complete an assessment within 30 calendar days. The OAIC treats that as a maximum, not a target. Once you know it's an eligible breach, you must notify the people at risk and the Commissioner as soon as practicable. Knowing what personal data you hold, where it lives and who can reach it is what makes that possible under pressure.
An illustrative example
Imagine a retailer whose sales reports never match between finance and merchandising. A governance effort might start by appointing an owner for sales data, agreeing one definition of net sales, documenting it in a glossary and adding automated checks to the pipeline. Within a few months, the reports agree and the monthly reconciliation effort largely disappears.
Tools that help
Platforms such as Microsoft Purview and OvalEdge support cataloguing, lineage, classification and quality monitoring. In Microsoft Purview's Unified Catalog, for example, data is organised into governance domains (such as Finance or Marketing), related tables, files and reports are grouped into data products that people can find and request access to, and data quality rules produce scores at the asset, data product and domain level. Tools work best, though, once roles and processes are clear. Our Microsoft Purview vs OvalEdge comparison covers how the two differ.
Our data governance consultants help organisations put practical governance in place, and our Data Governance Quick Start package gets the foundations set up in four weeks. You may also like our article on data strategy versus data governance.